
Enable and Operate Sophos Firewall Central Reporting
With Central Firewall Reporting, the Sophos Firewall sends selected log data to Sophos Fusion. This allows reports to be centrally evaluated, stored, and shared with others if needed.
This article explains how to enable Central Reporting, what points should be checked beforehand, and how to verify if log data is arriving in Sophos Fusion.
Which Logging Article Fits?
Central Firewall Reporting is a component of the log architecture. Depending on the goal, a different entry point may be more suitable:
- Evaluate reports and firewall logs in Sophos Fusion: This article
- Send a local firewall report as a PDF every day or every week: Schedule Sophos Firewall reports and send them by email
- Check individual connection, Rule ID, NAT ID, or packet flow live: Test Sophos Firewall Rule with Log Viewer, Policy Tester, and Packet Capture
- Send logs to your own SIEM or log server: Send Sophos Firewall Syslog to SIEM
- Classify local log files, services, and Advanced Shell: Sophos Firewall Troubleshooting: Services and Logs
- Secure logs for Sophos Support or Avanet: Secure Sophos Firewall Logs for Support or Analysis
- Track configuration changes: Check Sophos Firewall Audit Trail Logs
- Evaluate NDR or Active Threat Response hits: Operate Sophos Firewall NDR and Active Threat Response
- Analyse NetFlow v5 records from specifically logged firewall rules: Configure and test NetFlow on Sophos Firewall
- Analyse traffic samples and interface counters: Configure sFlow Monitoring on Sophos Firewall
- Review system status, security reports, and admin events on a recurring basis: Daily Sophos Firewall admin checklist
This distinction is important: Central Reporting is good for reports, search, and history in Sophos Fusion. For live troubleshooting on the firewall, support log packages, SIEM correlation, or flow analysis, other tools are needed.
When Central Firewall Reporting is Helpful
Central Firewall Reporting is particularly useful when multiple firewalls are operated or when reports need to be regularly evaluated.
Typical examples:
- Central overview of multiple firewalls.
- Regular reports for management or operations.
- Analysis of web, application, IPS, VPN, or network events.
- Longer retention and easier search in log data.
- Support in troubleshooting and security reviews.
For pure live analysis directly on the firewall, local logs are often sufficient. For long-term evaluations, Central Reporting is significantly more convenient. If logs are to go to your own SIEM or an external log server, Send Sophos Firewall Syslog to SIEM is more suitable.
Prerequisites
Before activation, check the following:
- The firewall is registered in Sophos Fusion.
- The firewall has internet access to the required Sophos services.
- DNS and time are functioning correctly.
- The active license supports the required reporting function.
- The firewall is visible in Sophos Fusion.
- An account with the Super admin role in the relevant Sophos Fusion tenant (formerly Sophos Central) is available to approve reporting after local enablement.
If the firewall is not yet registered in Sophos Fusion, this must be done first. Without registration, Central Firewall Reporting cannot be activated.
Local WebAdmin permissions, registration using an OTP or credentials, and subsequent service approval are separate steps. Neither local admin rights nor successful registration replace approval by a tenant Super admin. Do not share that account’s credentials with OTP operators; the Super admin approves the service using their own account.
Activate Central Reporting
Central Firewall Reporting is activated in two places: first on the firewall and then in Sophos Fusion.
- Log in to the WebAdmin of the Sophos Firewall.
- Open System > Sophos Central.
- Under Sophos Central registration, check if the firewall is registered.
- If the firewall is not yet registered, select Register and log in with the appropriate Sophos Fusion account.
- Activate Sophos Central services or select Configure if the service is already active.
- In Firewall Management and Reporting from Sophos Central, select Use Sophos Central reporting.
- Optionally select Use Sophos Central management if the firewall should also be centrally managed.
- Optionally select Send configuration backup to Sophos Central if configuration backups should be stored centrally while Central Management is enabled.
- Select Apply.
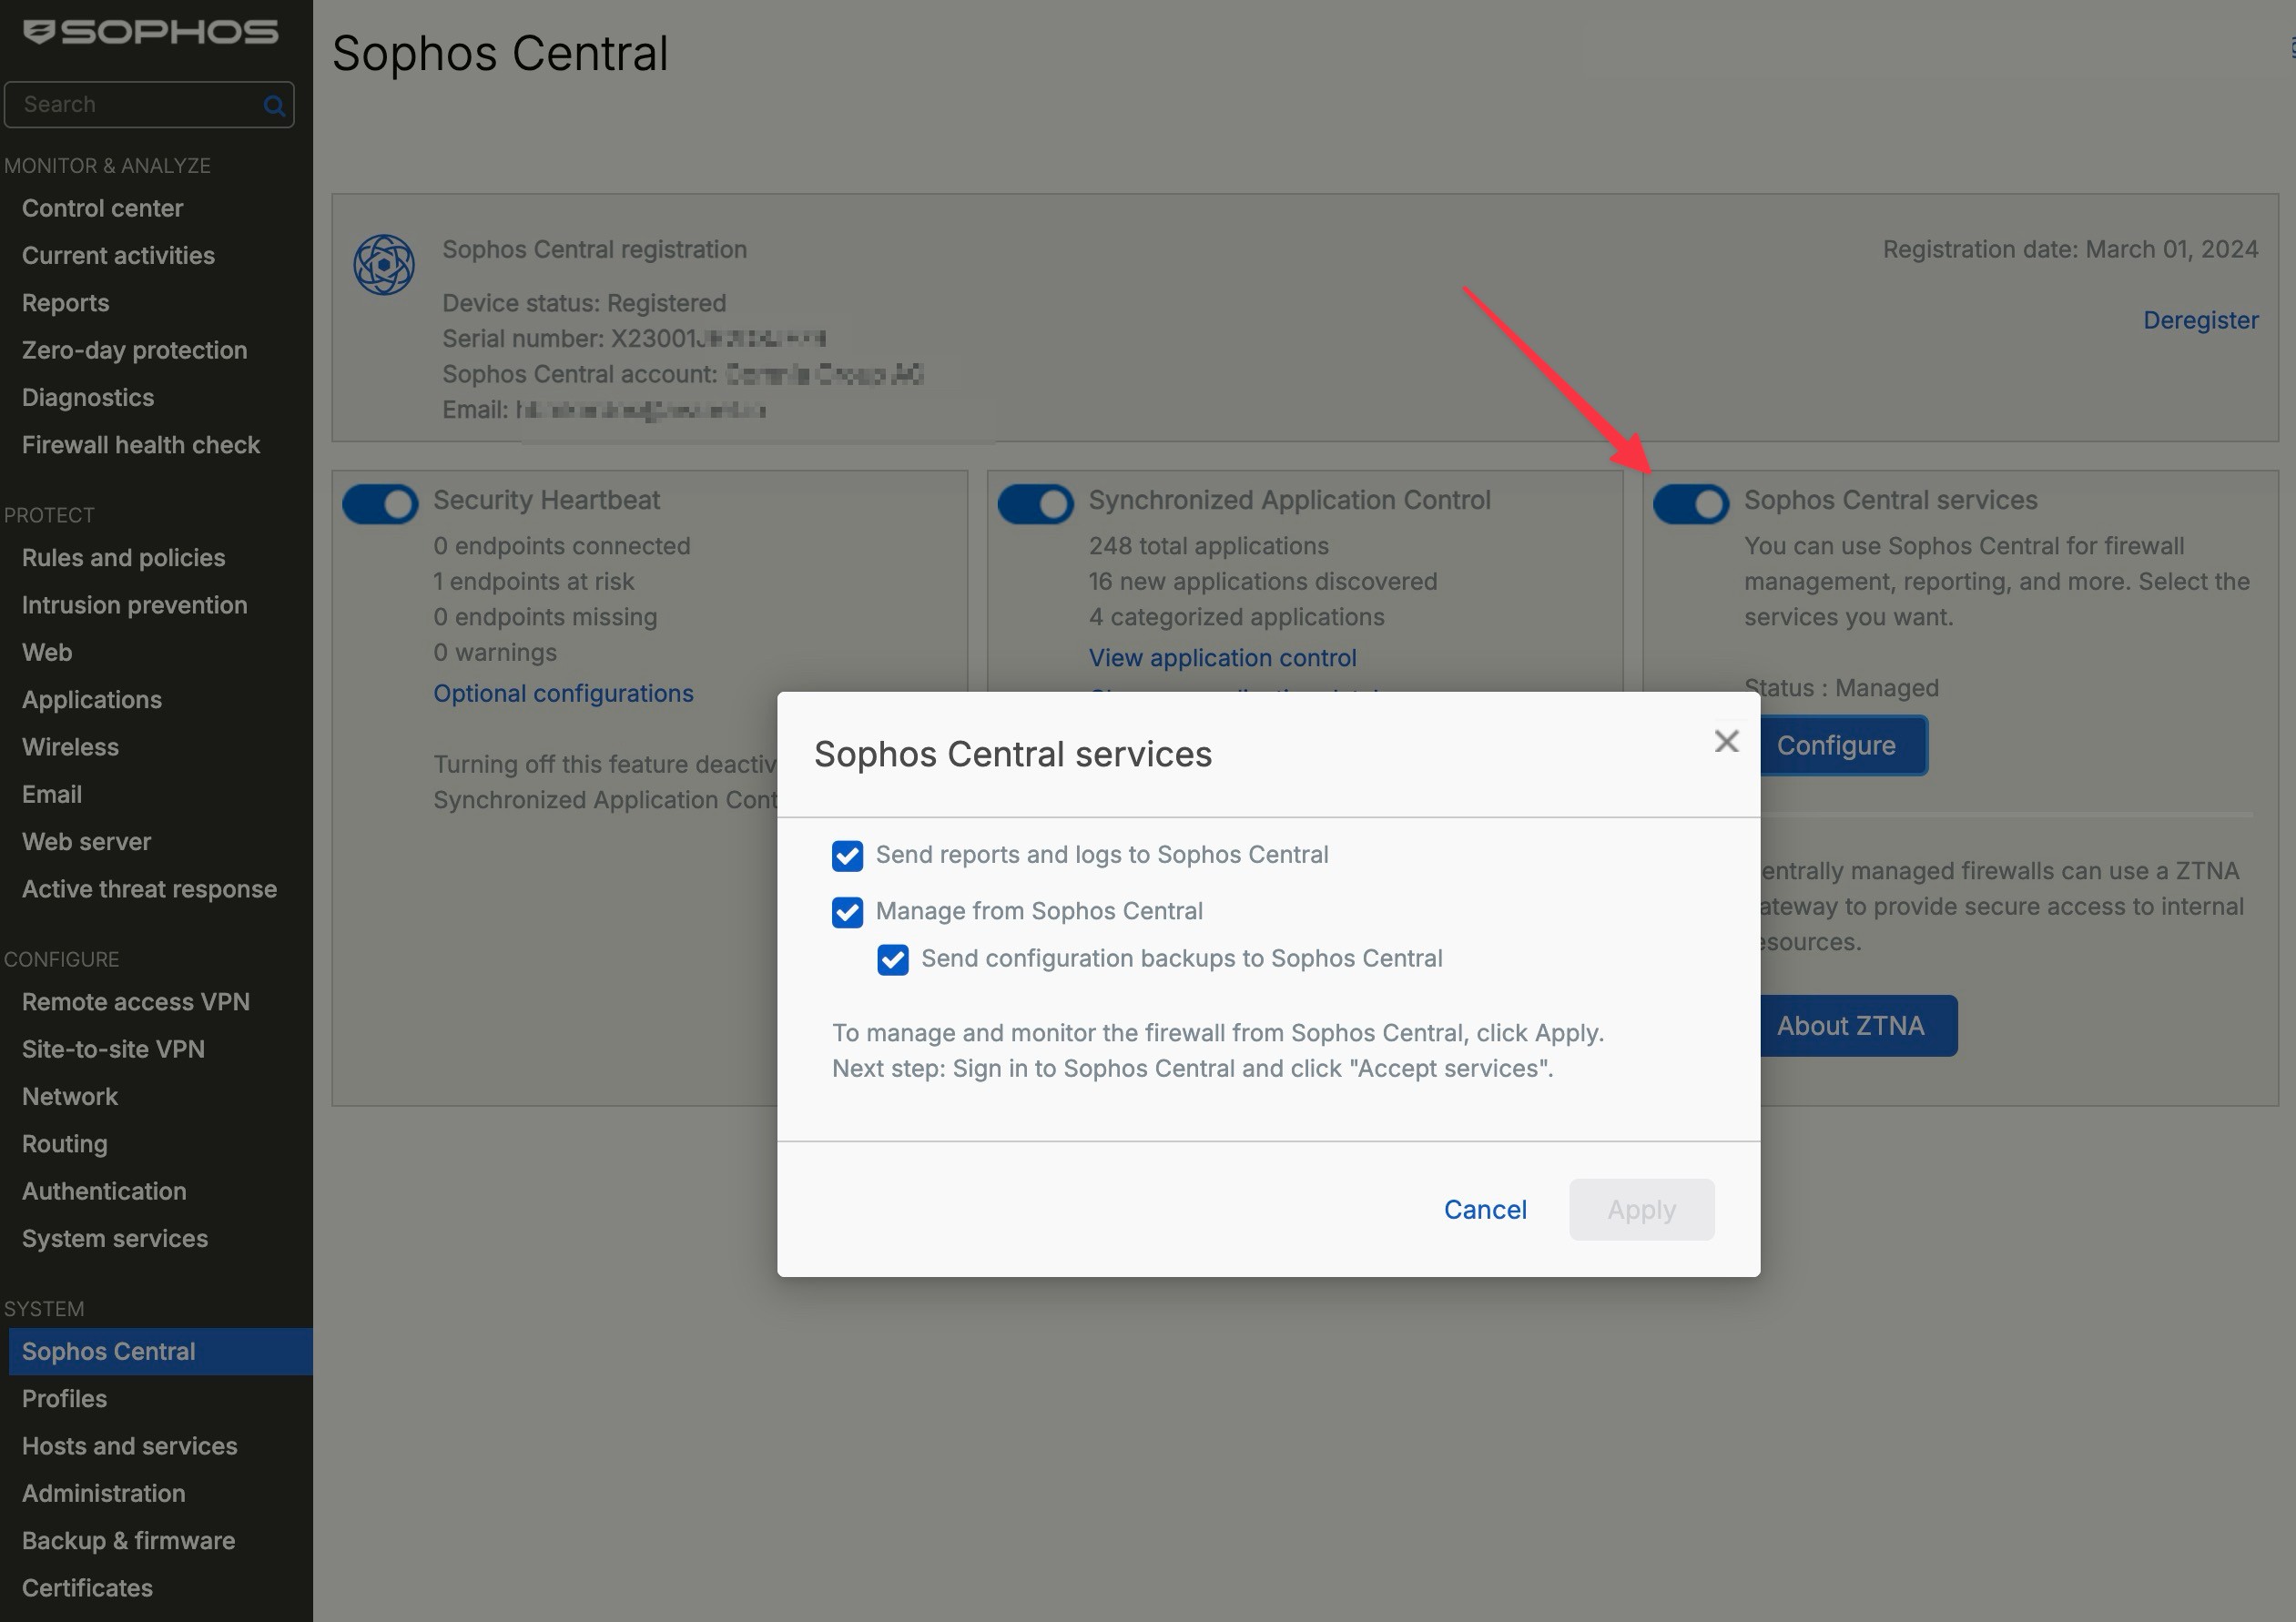
The screenshot still shows the former field name. In SFOS 22, the same reporting option is called Use Sophos Central reporting; use the current field name from step 6 when configuring it.
After saving, the service must be confirmed in Sophos Fusion:
- Log in to Sophos Fusion with an account that has the Super admin role in the relevant tenant.
- Open My Products > Firewall Management > Firewalls.
- Find the firewall with the status or symbol Approval pending.
- Select Accept services.
After activation, the firewall starts sending the selected log data to Sophos Fusion. Transfer and processing aren’t immediate: the firewall sends data at least every five minutes, and database processing in Central can then take another five to thirty minutes. Allow up to 35 minutes for the first check instead of immediately changing the configuration again.
What Data is Transferred
Which log types are sent to Sophos Fusion is defined directly on the firewall.
The menu path is Configure > System services > Log settings.
Under Log settings, Local reporting and Central reporting are separate columns. A log type can therefore be stored locally, in Central, or at both destinations. Central reporting doesn’t depend on Local reporting. However, the relevant firewall or SSL/TLS inspection rule must first generate the event with Log firewall traffic or Log connections.
The UI groups log types under Firewall, IPS, Antivirus, Anti-spam, Content filtering, Events, Web server protection, Active threat response, Wireless, Heartbeat, System health, Zero-day protection, and SD-WAN. For VPN or administrator events, select the relevant entries within these groups and then generate a specific event to confirm that the expected record arrives.
For Wireless, Access points & SSID is turned off under Local reporting by default because these logs don’t appear in the local Log Viewer. They can still be sent to Sophos Fusion or a syslog server.

Not every environment needs to send all data to Sophos Fusion. In production environments, check which log types are actually needed and whether internal data protection requirements are met.
⚠️ The more log types are sent to Sophos Fusion, the faster the available storage is consumed. In production environments, select only the logs needed for operations, security, and compliance.
The difference between logs and reports is also important: The selection under Central reporting controls which event logs are sent to Sophos Fusion. This selection does not automatically replace local on-box reports and is not the same as a complete support log package.
How Long Sophos Stores the Logs
The retention period depends on the license and available storage. Important: The limit that is reached first always applies. When the storage is full, older data is removed according to the FIFO principle.
- Central Firewall Reporting without additional reporting license: Up to 7 days. Available with active firewall subscription. Storage is model-dependent and limited.
- Xstream Protection Bundle: Up to 30 days. This corresponds to a limited Central Firewall Reporting Advanced entitlement.
- Central Firewall Reporting Advanced: Up to 365 days. Each CFR Advanced licence increases the available storage by 100 GB. Firewalls with very high log volume may need more than one 100 GB unit to realistically reach the maximum retention.
Basic Reporting can generate reports in Central, but the firewall can’t be included in scheduled or group reports. The Xstream Bundle and CFR Advanced additionally allow PDF, HTML, and CSV downloads as well as saved, scheduled, and group reports. The licence tier therefore affects not only retention but also the repeatable reporting workflow.
The Central Firewall Reporting Advanced license can be obtained from Avanet: Central Firewall Reporting Advanced. The data sheet describes Central Firewall Reporting additionally as cloud-based reporting with search, reports, and up to 365 days retention: Sophos Central Firewall Reporting Data Sheet.
For all variants, storage and maximum retention work together. As soon as one limit is reached, older data is removed according to first-in-first-out. A licence with long maximum retention therefore does not automatically guarantee that every firewall actually keeps data for that long.
Manage reporting licenses and stored data
Under Profile > Licensing > Product licenses > Central Firewall Reporting > Manage, use plus or minus to assign or remove reporting licenses for a firewall. The view shows the device, IP address, model, license type, occupied Central storage, average daily upload, retention period, and oldest retained date. Firewalls can be searched by serial number.
The action menu contains several commands with very different effects:
- Associate licenses and data with replacement device transfers the reporting license and existing data to a replacement device.
- Reclaim all licenses (convert to basic) returns the firewall to Basic Reporting and deletes its already stored logs and reports.
- View device reports opens Report Hub for this device.
- Delete log data irreversibly deletes all Central log data for the firewall. The action is logged and can include a reason.
- Delete log data and unregister from Sophos Fusion additionally removes the Central registration. This action is also irreversible and logged.
Reclaiming a license is therefore more than a commercial change. Before Reclaim, deletion, or unregistering, export required reports, approve the retention decision, and define the later log source or replacement registration.
Plan Retention and Responsibility
Central Reporting should not only be activated technically. It should be clear in advance which log types are really needed, how long the data must be available, and who regularly checks reports.
For operations, these points should be documented:
- Purpose of data collection: Troubleshooting, security review, audit, management report, or support.
- Required log types, for example, firewall, web, IPS, VPN, or Active Threat Response.
- Desired retention period and appropriate license.
- Owner for report templates, planned reports, and escalations.
- Data protection or compliance requirements for user, URL, and network data.
- Decision on whether syslog or SIEM is additionally needed.
If logs are relevant for incident response or audits, you should not wait until a disruption to check if the data is complete. A short monthly control report is often enough to see if the expected log types are arriving and if the storage consumption matches the planned retention.
Check Log Arrival
After activation, the data does not always appear immediately in Sophos Fusion. A few minutes delay should be planned.
Then check these points:
- Log in to Sophos Fusion.
- Open My Products > Firewall Management > Report Hub.
- Select the affected firewall.
- Check visibility of current events.
- Create a simple report as a test.

If no data is visible, you should first check connection, license, and log settings.
Validate Reporting Specifically
A report with data does not yet prove that Central Reporting is fully usable for operations. After activation, at least a small validation plan should be worked through.
Recommended tests:
- Check firewall rule logs: Trigger a logged test rule and search for source, destination, and Rule ID in the Report Hub. The event should be visible with the correct firewall, time, and action.
- Check web or application events: Perform a known web or Application Control test. The category, user, or client IP should appear in the appropriate report.
- Check VPN events: Establish and disconnect a test connection. Login, connection, and disconnection should be visible in the selected timeframe.
- Compare the time basis: Compare firewall time, the Sophos Fusion timeframe, and the local timezone. Events should not appear in an unexpected timeframe.
- Assess retention: Check older data in the Report Hub and observe storage consumption. The available retention should match the license and internal purpose.
- Review log settings: Under System services > Log settings, verify that firewall rules generate Log firewall traffic and that SSL/TLS inspection rules have Log connections enabled when needed.
For multiple firewalls, you should also check if hostname, serial number, model, or location are clearly identifiable. Otherwise, a later security or support case becomes unnecessarily tedious because events are present but cannot be quickly assigned to the correct appliance.
Create a Reproducible Report
Under My Products > Firewall Management > Report Generator, first select the firewall, then a Report template and the Time frame. You can combine filters under Query; every filter condition must match. Select Generate to create the report.
For a reproducible functional test, use the Firewall template, a short time frame, and Source IP = 192.0.2.25, for example. 192.0.2.25 is a documentation address and must be replaced with the actual test client IP. Equality queries are case-sensitive. For a partial match or subnet, use the ~ operator with *, such as Source IP ~ 192.0.2.*. A time frame longer than 30 days may place the report in the Queue; queued reports are automatically deleted 24 hours after generation.
With Xstream or CFR Advanced, you can use Save Template to retain the completed filter or Schedule to export it as PDF, HTML, or CSV. A template stores the columns, chart, and filters, but not report data. Export files appear under Scheduled Exports and are automatically deleted after 90 days. If a report contains personal data, prefer the access-protected email link to an attachment.
Useful reports for operations:
- Top blocked applications.
- Web categories with high traffic.
- VPN connections.
- IPS events.
- NDR and Active Threat Response events.
- Top rules by hit count.
- User or host-related evaluations.
If web categories are not only to be evaluated but also actively reported on critical accesses, Use Sophos Firewall Web Categories and Instant Alerts is suitable.
For recurring operational checks, you can schedule reports or save them as templates. If NDR Essentials or NDR Active Threat Intelligence is used, the process from Operate Sophos Firewall NDR and Active Threat Response should be linked with Central Reporting or SIEM evaluation.
Pause Reporting Without Deleting Registration or Data
For a controlled pause, first record the enabled entries in the Central reporting column, for example with a screenshot. Then go to System > Sophos Central > Sophos Central services > Configure and turn off Use Sophos Central reporting. The firewall remains registered with Sophos Fusion; Central Management and configuration backups are separate services. Turning reporting off doesn’t itself invoke a data-deletion action, but existing data remains subject to the licensed retention and storage limits and continues to age out according to FIFO.
To resume later, turn on Use Sophos Central reporting again, have a Super admin of the relevant Sophos Fusion tenant accept Approval pending with Accept services if required, and restore the same log selection under Configure > System services > Log settings. Trigger the defined test event again and find it in Report Hub.
⚠️ Reclaim all licenses (convert to basic), Delete log data, and Delete log data and unregister from Sophos Fusion aren’t rollback options for a reporting pause. Reclaim deletes the firewall’s stored logs and reports. Delete log data deletes its Central log data, while Delete log data and unregister from Sophos Fusion also removes the firewall from Central. The deletion actions can’t be undone.
Troubleshooting
No Data in Sophos Fusion
Check whether the firewall is online and can communicate with Sophos Fusion. Also check DNS, the default gateway, and time. Then go to System > Sophos Central > Sophos Central services > Configure and confirm that Use Sophos Central reporting is still enabled and that no service approval is pending in Sophos Fusion.
If the firewall is managed via Sophos Fusion but does not deliver reports, management access and reporting should still be checked separately. A functioning Central login to the firewall does not automatically prove that all selected log types also arrive in the Report Hub.
Only Individual Log Types Missing
Under Configure > System services > Log settings, check the Central reporting column. Local reporting is an independent destination and doesn’t need to be enabled for transfer to Central.
Particularly often, it is not the Central connection that is missing, but the actual event:
- Firewall rules do not have Log firewall traffic activated.
- Under System services > Log settings, the column Central reporting is not active for the log type.
- The chosen report considers a different timeframe or a different firewall.
- User or web reports remain empty because the firewall does not see user identity.
- NDR or Active Threat Response events are missing because the function is globally active but not fully integrated into rules or logging.
Reports Show Old Data
Central Reporting does not work in real time. Check the selected timeframe in the report and wait a few minutes before changing the configuration again. A delay is normal for new events because the firewall sends data periodically and Sophos Fusion processes it afterwards.
If data consistently appears delayed or incomplete, you should not repeatedly reset the same settings. A defined test with time, source, destination, log type, and expected firewall is better. Then Log Viewer, Central Report Hub, and, if necessary, syslog or local logs can be cleanly compared.
Too Much or Too Little Data
Adjust the log selection and filters in Sophos Fusion. For audits or support cases, it may be useful to collect more data. For normal operations, targeted reports are often sufficient.
Too much data is not only a storage problem. Evaluation also becomes more difficult if no one regularly checks the reports. Too little data is critical if exactly firewall, VPN, web, or IPS events are missing in an incident. Therefore, the log selection should not be set once on the side but should match the planned use cases.
Check Central Reporting After Changes
After certain changes, Central Reporting should be consciously checked:
- Firmware update or rollback.
- HA failover or appliance replacement.
- Change to Sophos Central registration or services.
- New firewall rules, web policies, IPS policies, or VPN profiles.
- Change of license, bundle, or reporting advanced entitlement.
- Reimage, restore, or migration to a new model.
For central changes via Sophos Fusion, the Sophos Fusion Firewall Management Task Queue is also suitable. There you can see if Central has successfully applied a change to the firewall. For local configuration changes, you should include Audit Trail Logs and for rule problems, the Log Viewer with Policy Test and Packet Capture.
Secure Logs for Support Cases
Central Reporting does not replace every local log analysis. If Sophos Support or Avanet requires a complete local log collection, you can additionally export the firewall logs.
For support cases, you should therefore clearly separate:
- Show history, reports, affected users, or top events: Central Reporting
- Check individual connection live: Log Viewer, Policy Test, and Packet Capture
- Check service errors, debug logs, or module status: Local log files and service logs
- Provide a complete package for Sophos Support or Avanet: Local log export or Consolidated troubleshooting report
In practice, Central Reporting is often the best starting point because you can narrow down time windows, firewall, user, source IP, and affected rule faster. For the actual root cause analysis, however, local logs are often additionally needed, especially for VPN, WAF, IPS, HA, system, or service problems. The process is described in Secure Sophos Firewall Logs for Support and Analysis. For module and service assignment, Sophos Firewall Troubleshooting: Services and Logs is also helpful.
Operational Recommendation
Central Firewall Reporting is particularly useful for multiple firewalls or regularly needed reports. For troubleshooting, it is helpful to use local logs and Central Reporting together: Central for overview and history, local logs for detailed analysis directly on the firewall.
In productive environments, Central Reporting should be treated like an operational process:
- Select log types according to purpose, do not just activate everything.
- Assign a report owner who really checks planned reports and noticeable trends.
- Regularly check storage consumption and the oldest available data.
- Conduct a short reporting test after firmware updates, HA failover, restore, or license change.
- Define at least one incident test: find affected source IP, Rule ID, VPN user, or web category in the Report Hub.
- Decide for security operations which events remain in Central and which additionally go to a SIEM.
For small environments, a monthly control look at firewall, web, VPN, and IPS reports is often sufficient. For multiple locations, MSP operations, or compliance requirements, a fixed review appointment should exist. Then it is checked whether expected log types are still arriving, whether storage and license match the desired retention, and whether reports can quickly answer the right questions in an emergency.
If logs are relevant for security operations, incident response, or compliance, it should also be decided whether Syslog to a SIEM is needed. Central Reporting is very useful for Sophos Fusion evaluations but does not automatically replace a cross-vendor log archive or a SOC process.