
Reinstall Sophos Firewall OS: USB reimage
A reimage fully reinstalls Sophos Firewall OS. The procedure is intended for recovery situations, lab systems, model changes or a clean reinstall. For normal version changes, a firmware update through the WebAdmin interface is usually the better choice.
⚠️ Important: A reimage overwrites the firewall completely. Configuration, local logs, certificates, reports and stored account data are no longer present on the device afterwards. Before starting, store a backup externally together with its Encryption password and the Secure Storage Master Key (SSMK) associated with that backup. Backups created after an SSMK is set or changed can only be restored with that exact key, so retain earlier keys as well.
Reimage, firmware update or factory reset?
| Method | Purpose | Typical use |
|---|---|---|
| Firmware update | Update SFOS to another version | Normal maintenance through Backup & Firmware > Firmware |
| Rollback | Return to a previously installed firmware version | Problems after an update, as long as the previous firmware is still available |
| Factory Reset | Reset configuration | Device remains on the installed SFOS version, configuration is lost |
| Reimage | Reinstall SFOS from a USB stick | Defective system, clean reinstall, incompatible version change or recovery |
Rollback also rolls back the configuration: Sophos Firewall stores the active and previous firmware with their corresponding configurations in independent partitions. Settings are not shared between the partitions. Rolling back to the previous firmware therefore also restores its earlier configuration, not the current configuration. Account for this when choosing a recovery path; this does not guarantee a tested rollback for your environment.
For a normal update, first check Sophos Firewall: perform SFOS firmware update. A Factory Reset is also not the same as a reimage: it resets the configuration, but does not remove all local data like a full reinstall. The public SFOS 22 help contradicts itself about the SSMK: the dedicated reset page says it is retained, while the general firmware page says it is removed. Therefore, store the key externally before every reset and verify its state afterward. If the firewall really needs to return to a clean default state including logs, reports and local operational data, reimage is the more suitable path. For XGS Appliances with damaged firmware, Sophos refers to the reimage procedure because the SFLoader recovery procedure isn’t available on XGS Appliance.
Reset Sophos Firewall to factory settings explains the safe WebAdmin process and the different hardware sequences for XGS Appliance models.
When not to start a reimage
A reimage is the hard recovery option. If normal administrative access is still possible, first check whether a less invasive approach is sufficient.
| Situation | Better check first |
|---|---|
| WebAdmin hangs, but traffic continues | Restart WebAdmin GUI deliberately |
| A single service does not respond | Restart Sophos Firewall services safely |
| Firmware update is planned | Firmware update and rollback plan instead of reimage |
| Configuration should be deleted | Factory Reset may be enough if SFOS itself is healthy |
| Storage space or reports are the problem | Check storage, reports and logs |
| Support case is still running | Save logs, support archives and current errors first |
Reimage makes sense if the operating system is damaged, a clean rebuild is required, or Sophos Support or the recovery plan specifies this path. For normal maintenance, individual GUI problems or unclear performance issues, it is usually too early.
If the firewall starts in Failsafe mode, record the detected cause before a Reboot, Factory Reset, or reimage. Check Sophos Firewall in Failsafe mode shows the show failure-reason command and the safe next decisions.
Back up before the reimage
Before a production reimage, prepare these points:
- Download a current configuration backup and store it safely.
- Document the Secure Storage Master Key if the backup contains encrypted account data.
- Check licence status, serial number and Sophos Fusion (formerly Sophos Central) assignment.
- Document model, revision, current SFOS version, build, target version and backup version.
- Note WAN data, VLANs, static routes, VPN parameters and special HA information separately.
- Plan a maintenance window because the firewall does not protect or process traffic during the reimage.
- Ensure local access to the appliance, power supply, USB port and management port.
- Check the restore process beforehand, especially for HA clusters and critical VPN sites.
- Save logs or support archives if the cause must still be analysed later.
The relevant basics are covered in Sophos Firewall: create and restore backups, Sophos Firewall: SFOS 22 upgrade check and Sophos Firewall HA cluster: Active-Passive, Active-Active and Auxiliary Appliance.
If the reimage is part of an RMA or HA scenario, this documentation becomes even more important. Then not only the main version matters, but also the build. A replacement device should match the healthy firewall or be deliberately brought to the target version before backup, licence transfer and HA reconfiguration begin.
Clarify restore compatibility in advance
The most important part of a reimage is not writing the USB stick, but the successful restore afterwards. A backup should not be assessed for the first time only after the reinstall.
Clarify beforehand:
| Item | Why it matters |
|---|---|
| Backup version | A backup cannot be restored arbitrarily to every older or newer SFOS version. |
| Target model | Port count, interface names and model class affect restore and port mapping. |
| Secure Storage Master Key | Without the matching SSMK, protected account data is missing after restore. |
| Licence and account | After reimage or model change, the firewall must be licensed and assigned correctly again. |
| HA role | In clusters, it must be clear whether Initial Primary or Auxiliary is being rebuilt. |
| Legacy configuration | Old Remote Access IPsec or upgrade blockers should be known before restore. |
For hardware replacement, XG-to-XGS Appliance migration or restore to another model, also check whether the Backup-Restore Assistant is available and whether port mapping is correct before the final restore. The process is described in Sophos Firewall backup and restore.
For HA and RMA, the rule of thumb is: firmware version and build of the involved devices are checked before restore. If the required old firmware version can no longer be downloaded normally, do not improvise; involve Sophos Support or the existing support process.
Requirements
- Sophos hardware appliance. The USB and LED procedure below is written for this case.
- USB stick with at least 4 GB storage.
- Windows, macOS or Linux computer to create the bootable USB stick.
- Tool for writing the ISO image, for example balenaEtcher.
- Local access to the appliance.
- Optional: USB-to-Micro-USB cable or RJ45-COM adapter for status messages and troubleshooting through the serial console.
A support subscription isn’t required to reinstall the same firmware version. If the reimage moves the firewall to another firmware version, the licensing and support conditions for firmware upgrades apply.
Treat software and virtual appliances separately
Sophos also permits reimaging software and virtual appliances, but the image and installation method differ. A software appliance on your own x86-64 hardware uses the SW ISO. Installation formats and repartitions the disk, deleting the existing operating system. The SFOS 22 minimum requirements are Legacy BIOS, 4 GB RAM, a 32 GB HDD or SSD and two network interface cards; Sophos recommends 64 GB disk capacity.
A virtual appliance instead uses the package for its hypervisor, such as VI-22.0.2_MR-2.VMW-546.zip for VMware. Deploy it using the instructions for that platform and use only the built-in SFOS feature for backup and restore; according to Sophos, hypervisor snapshots and third-party backups are not a supported substitute. The physical USB and XGS Appliance LED steps below therefore do not apply unchanged to virtual systems.
Before upgrading to SFOS 22.0 or later: Unclaimed software and virtual appliances, as well as Azure and AWS BYOL firewalls, must first be claimed in the Sophos account (Sophos Fusion or Sophos Central). This is an upgrade preflight requirement that must be met before the version change; later registration during setup is not a substitute. It does not establish a general claiming requirement for every hardware reinstall of the same firmware version.
1. Download the correct SFOS installer image
The installer image is obtained from the official Sophos download page:
- Download the current Sophos Firewall installer.
- For Sophos hardware appliances, select the required SFOS version under Hardware Installers.
- Accept the licence terms and download the ISO image.
Hardware appliances usually use an image with the HW prefix. Software and virtual appliances use other image types. What matters is that platform, target version and restore plan fit together. A wrong image is not a small cosmetic mistake; it can stop the recovery workflow.
Installer image filename
Example available on 5 September 2026: HW-22.0.2_MR-2-546.iso
| Component | Meaning |
|---|---|
HW | Installer for Sophos hardware appliances |
22.0.2 | SFOS version |
MR-2 | Maintenance Release 2 |
546 | Build number |
.iso | ISO image for USB stick or software installation |
The most important filename components:
Platform or appliance type
- HW: ISO image for Sophos hardware appliances. This variant is usually required for reimaging an XGS Appliance.
- SW: ISO image for Sophos Firewall as a software appliance.
- VI: Image package for Sophos Firewall as a virtual appliance.
- AMI: Image for Amazon AWS.
- AZU: Image for Microsoft Azure.
Virtualisation platform for VI files
- HYV: Microsoft Hyper-V.
- KVM: KVM.
- VMW: VMware Hypervisor.
- XEN: Xen.
Release type
- GA: General Availability. This is a generally available major or interim version, often with new functions.
- MR: Maintenance Release. An MR mainly contains fixes, stability improvements and security adjustments within an existing version.
File extension
- .iso: ISO image that can be written to a USB stick or used for software appliances.
- .zip: Archive with image files for virtual appliances.
- .sig: Signed image for certain appliance models or update scenarios.
For production systems, choose the target version based on support status, backup compatibility and the recovery plan, not simply the highest filename available. In a support case, use the version agreed with Sophos.
For an XGS Appliance reimage, a file such as HW-22.0.2_MR-2-546.iso is an example of the relevant image type. SW, VI, AMI or AZU are intended for other platforms and should not be used for a hardware appliance.
Check download authenticity and integrity
The HW prefix alone does not confirm that an image supports the specific device. The Hardware Installers index lists hardware series or platform images and their builds; use it to select the planned series or platform and target build, not to infer that an exact appliance model is listed. If applicability to the exact model or build is uncertain, stop and resolve it through Sophos support or the existing Avanet lifecycle context before downloading or installing.
Use four checks for a controlled download:
- Obtain the image only through the HTTPS download linked above on
download.sophos.com, not from a mirror, forum or old local archive. - Compare the filename prefix, version, release type and build with the reimage and restore plan.
- Record the filename, file size and a locally calculated SHA-256 value in the change or recovery record.
- If the portal or support provides a checksum for that exact file, compare it character for character. Discard and download the file again if it differs.
Calculate SHA-256 on Windows with certutil -hashfile HW-22.0.2_MR-2-546.iso SHA256, on macOS with shasum -a 256 HW-22.0.2_MR-2-546.iso, or on Linux with sha256sum HW-22.0.2_MR-2-546.iso. A locally calculated hash detects later changes between download, storage and use, but without a trusted reference value it does not prove origin. Authenticity therefore still depends on the official HTTPS download and, when available, the separately supplied vendor checksum.

2. Create a bootable USB stick
The USB stick is formatted when the ISO image is written. All existing data on the USB stick is lost.
- Insert a USB stick with at least 4 GB storage into the computer.
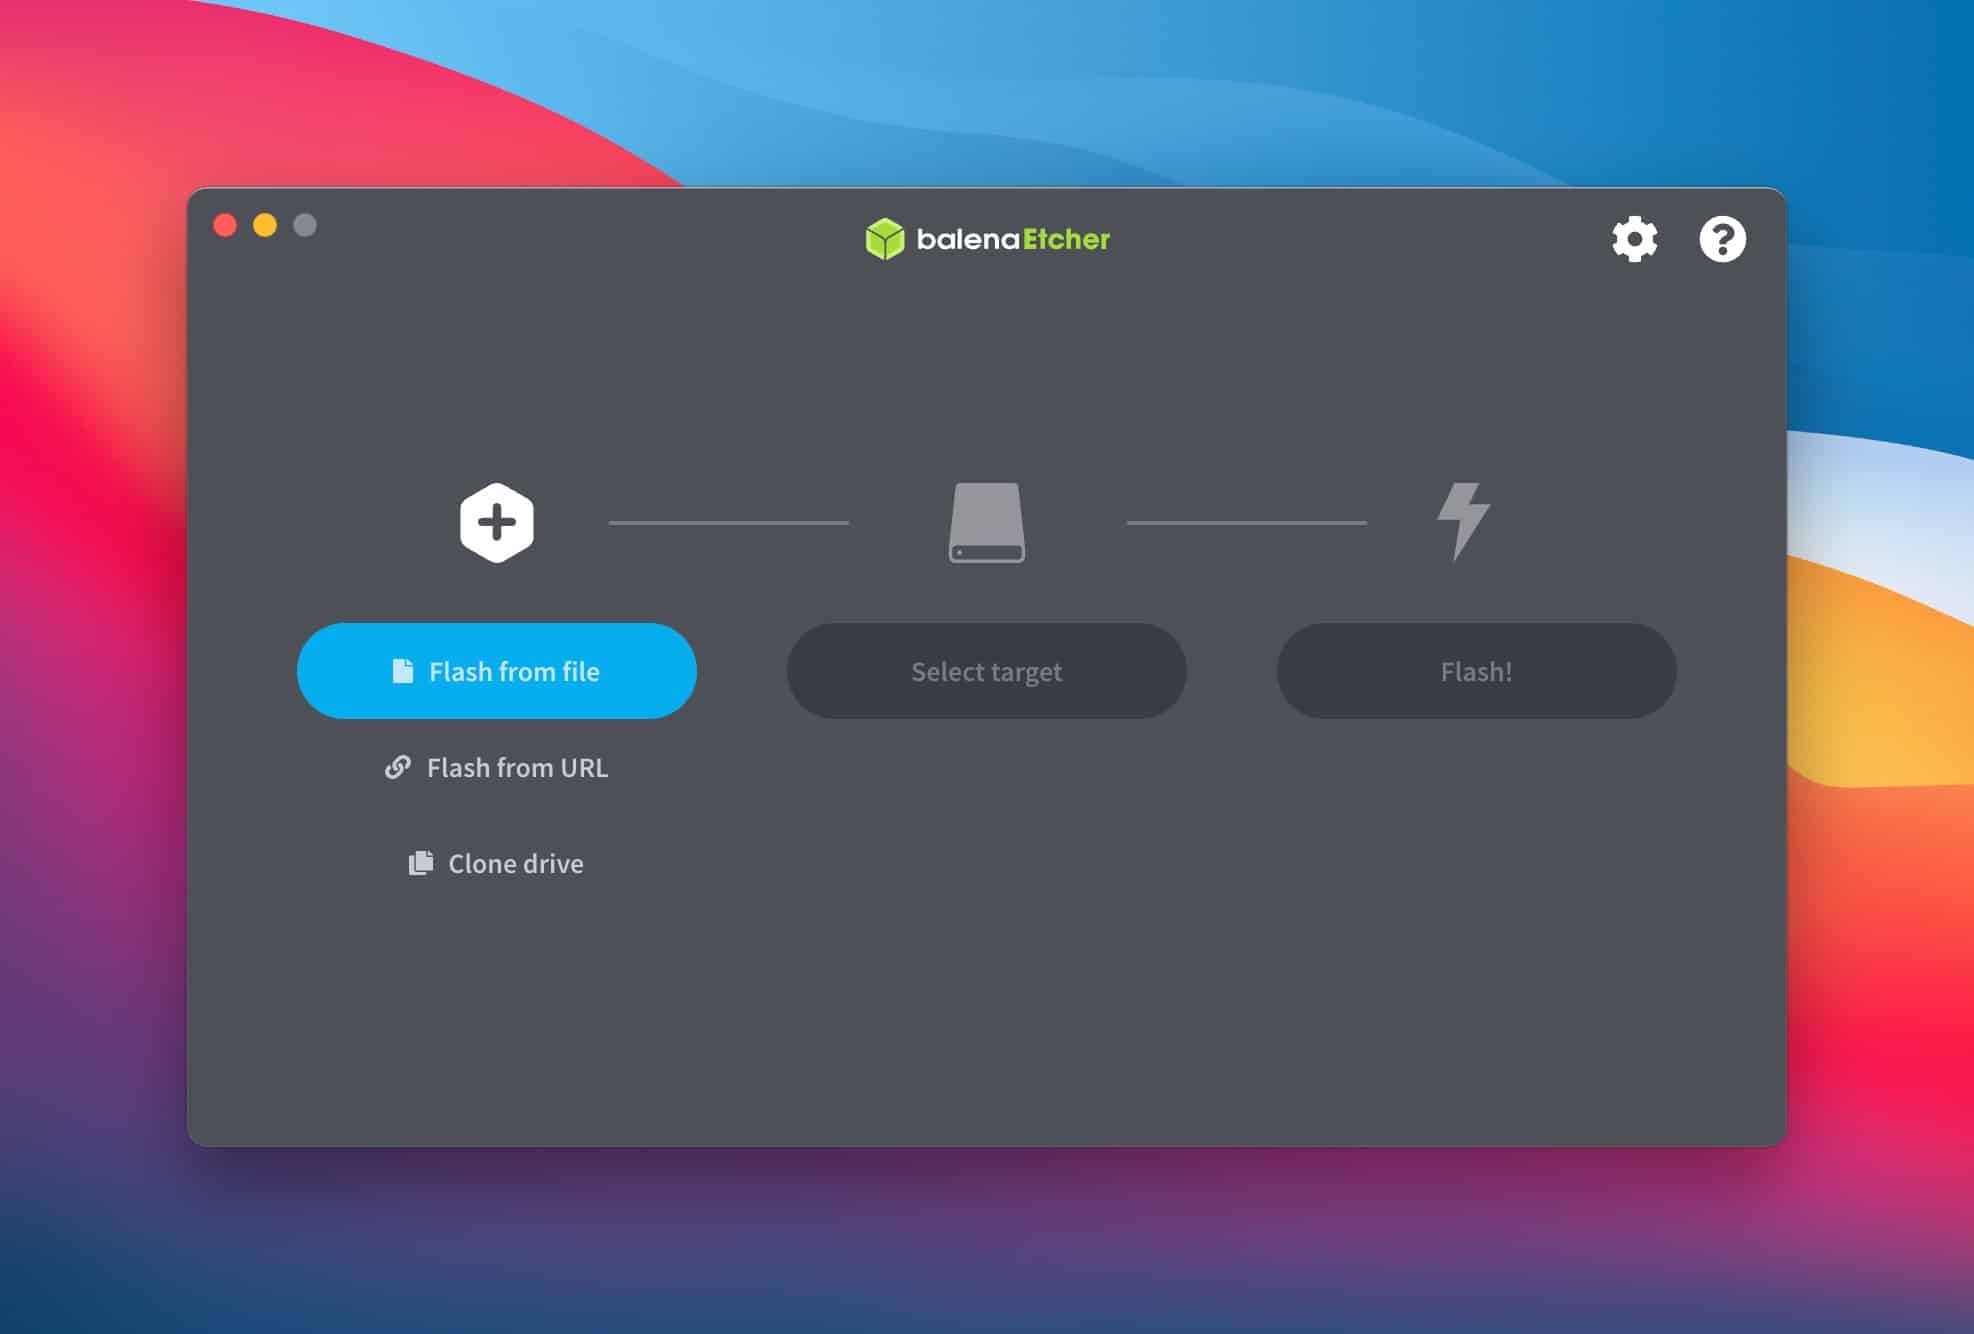
- Download and start balenaEtcher.
- Use
Flash from fileto select the downloaded SFOS ISO image. - Under
Select target, select the correct USB stick. - Use
Flash!to write the ISO image to the USB stick and wait for the subsequent validation to finish without errors. Do not copy the ISO to the stick as a normal file.
After writing, eject the USB stick cleanly. If macOS or Windows reports the stick as unreadable afterwards, this is not necessarily an error because the image was written for the appliance boot process.
3. Reinstall SFOS on the firewall
The reimage process runs directly on the appliance. The device must not be switched off during this process.
- Shut down the firewall completely.
- Optionally prepare monitor, LCD or serial console if the installation status should be observed.
- Insert the prepared USB stick into the firewall.
- Switch on the firewall.
- Wait until the Sophos Firmware Installer starts from the USB stick.
- Monitor the installation status depending on the appliance model.
- After successful installation, remove the USB stick.
- If the installer then asks for confirmation, restart with
y.
Status on XGS Appliance desktop models
According to Sophos, XGS Appliances don’t have a monitor connector. On desktop models, the reimage status is therefore shown by the status LED on the front. If you need more detail, use the serial console through the COM connector.
| LED status | Meaning |
|---|---|
| 🔴 Blinking red | Reimage is running |
| 🟢 Solid green | Reimage was successful |
| 🔴 Solid red | Reimage failed |
The reimage is only complete when the LED is solid green. While the LED is blinking red, the process is still running.
Status on XGS Appliance rack models
Rack appliances show the status on the integrated display. Typical messages are Installation in progress, Installation successful, Installation failed or Failsafe mode.
Status through the serial console
For additional diagnostics, a console can be connected. On current XGS Appliance desktop models, this is usually no longer a classic old RS-232 connector on the notebook, but a USB-to-Micro-USB cable connected to the firewall’s COM Micro USB port. The appliance still provides a serial console through it. On the admin computer, it appears as a COM port on Windows or as a tty device on macOS and Linux.
This is especially useful when no display connector is available, the LED remains solid red, booting from the USB stick is unclear, or installer and error messages need to be viewed directly. Many XGS Appliance models also have an RJ45-COM port. This RJ45-COM port is a console port, not a normal network port. If Micro-USB and RJ45-COM are connected at the same time, Micro-USB has priority.
Typical tools:
- Windows: PuTTY or another serial terminal client.
- macOS: Terminal with
screen, for examplescreen /dev/tty.usbserial-XXXX 38400. - Linux:
screen,minicomorpicocom.
Serial settings:
| Setting | Value |
|---|---|
| Baud rate | 38400 |
| Data bits | 8 |
| Parity | None |
| Stop bits | 1 |
4. Reach the firewall after the reimage
After the reimage, the firewall starts with the default configuration. The first access is typically through Port 1:
- Management IP:
https://172.16.16.16:4444 - Connection: connect the computer directly to Port 1 of the firewall
- Computer IP: set a suitable static IP in the
172.16.16.0/24network if access is not possible
Next, either complete basic setup and registration or restore an existing backup. The setup assistant registers the firewall and, after completion, upgrades it to the latest firmware. If a restore or HA plan depends on an exact version and build, don’t complete that step without accounting for the upgrade. A restore requires the Encryption password and, if the backup was protected with one, the matching Secure Storage Master Key.
A restore replaces the current configuration, deletes the backup stored on the firewall and restarts the device. 172.16.16.16 will not necessarily apply afterwards: use the management IP from the restored configuration for the next WebAdmin connection. You also need the backup’s Encryption password in addition to the SSMK. See the backup and restore guide for the full process and compatibility rules.
After the restore, at least these points should be checked:
- Interfaces, zones and VLANs.
- Default gateway, static routes and SD-WAN routes.
- Firewall rules, NAT rules and Webserver Protection.
- VPN connections and certificates.
- Licence status and synchronisation with Sophos Fusion.
- HA status if the firewall is part of a cluster.
- Logging, syslog targets and reporting.
For firewalls managed through Sophos Fusion, connect Sophos Firewall to Sophos Fusion also helps. For model changes or older devices, Sophos XG or XGS Appliance: choose the right appliance is relevant.
Do not treat HA and RMA like a standalone device
With a single lab device, a reimage is usually linear: write image, install, restore backup, test. With HA and RMA, the workflow is more sensitive. Beforehand, you must know which device is healthy, which role it has, which firmware version and build it runs, and whether Sophos Fusion or the licence transfer must be cleaned up first.
In Active-Passive environments, don’t simply connect a replacement device to the cluster with all cables attached. The role determines the procedure. When reimaging the Auxiliary, don’t restore the backup manually to that device; reimage it to exactly the same firmware version and build, reconfigure HA, and let it synchronize from the Primary. The official Primary procedure instead includes failover, restoring the newly installed device, and then rebuilding HA. Identify the Initial Primary, current Primary and Auxiliary before taking either path.
Sophos’s public HA reimage procedure explicitly covers Active-Passive only, not Active-Active. It requires both devices to run the same firmware version and build and gives different steps depending on the affected role. Do not transfer that sequence to Active-Active or an undocumented scenario; agree the support plan before erasing either device. Restoring an HA backup to the current Primary causes downtime without failover, and both firewalls must then be registered with Sophos Fusion again. If instead you restore a standalone-device backup to the current Primary, HA is disabled; after the reboot, check the HA status and deliberately rebuild the cluster if required.
Acceptance test after reimage and restore
After a successful login, a quick look at the dashboard is not enough. The firewall must serve the most important production paths correctly again.
Useful order:
- Check licence status, serial number, model and firmware version.
- Check interfaces, link status, VLANs and zones.
- Check WAN gateway, DNS, NTP and Sophos Fusion connection.
- Validate firewall rules, NAT rules and Log Viewer with a test client.
- Test site-to-site VPNs and remote access with real test targets.
- Check HA status and roles if a cluster is involved.
- Check syslog, Central Reporting, backups and scheduled reports.
- Remove old temporary access, local admin accounts or recovery exceptions.
If a restore was successful but traffic does not flow, do not immediately reimage again. Interface mapping, routing, NAT, Device Access, licence status or the peer return path are often involved. For analysis, use test firewall rule with Log Viewer, Policy Test and Packet Capture, understand NAT on Sophos Firewall and Sophos Firewall IPsec VPN troubleshooting.
Common problems
Firewall does not boot from the USB stick
Usually the USB stick was not written correctly, the wrong image was selected or the appliance does not start from the expected USB port. In that case, write the ISO again with balenaEtcher, test another USB stick and observe startup through monitor, LCD, status LED or serial console.
If the appliance still doesn’t detect the stick, press Delete during startup to open the BIOS. USB Key must be first in the boot order. If necessary, select the entry with the arrow keys and move it up with +. Then select Save and exit; the firewall restarts and should load Sophos Firmware Installer from the stick.
LED remains solid red
A solid red status LED means that the reimage failed. Do not simply continue productively by guesswork: check USB stick, image type, target model and installation message. If the error repeats, serial console and Sophos Support are more useful than several identical attempts.
Backup restore fails
Typical causes are an unsuitable target version, a damaged backup, a missing SSMK or a restore to another model without clean port mapping. First check backup version, target SFOS version, build, platform and SSMK. Then clarify whether a Restore Assistant, an intermediate step through another SFOS version or support is required.
WebAdmin is not reachable after reimage
After the reimage, the default configuration applies again. Connect the computer directly to Port 1, set a suitable IP in the 172.16.16.0/24 network and open https://172.16.16.16:4444. If that does not work, first check link status, local client IP, browser certificate warning and possibly boot status.
HA does not start cleanly after restore
With HA, the problem is often not the reimage itself, but role, firmware state, build, Initial Primary, Sophos Fusion assignment or restore order. Therefore, do not automatically reactivate HA; first document the state of both devices and compare it with the planned HA workflow.
Traffic does not flow after restore
If the configuration was restored but traffic does not work, interface mapping, zones, routing, NAT, Device Access, licence status or return paths are often involved. Log Viewer, Rule ID, NAT ID, Route Lookup and Packet Capture then help more than another reimage.
Licence or Sophos Fusion connection is missing
After reimage, RMA or model change, serial number, account assignment, licence transfer, DNS, gateway and Sophos Fusion connection must fit again. Only once the firewall is cleanly online should this be treated as a productive operating state.
Checklist
- Backup downloaded.
- Secure Storage Master Key available.
- Backup and target SFOS version documented.
- Firmware build and model revision checked, especially for HA or RMA.
- Serial number, licence status and Sophos Fusion assignment checked.
- Correct SFOS installer image selected.
- USB stick written successfully.
- Maintenance window and local access clarified.
- Appliance not switched off during the reimage.
- WebAdmin reached through Port 1 after restart.
- Backup restored and SSMK entered.
- Network, VPN, licence, Sophos Fusion and HA checked.
- Rule, NAT, routing and VPN tests performed with real clients.
- Temporary recovery access and notes cleaned up.